FRACTIONAL CISO · BOARD & INVESTOR ADVISORY · CYBER DUE DILIGENCE

Operating at the intersection of cybersecurity, strategy, technology and AI.

Serious about security. Pragmatic about business.

JandaSec combines senior CISO judgement with deep engineering, software development and cloud security expertise — from board-level decisions to the software, cloud and infrastructure behind them. From Fractional CISO leadership and pre-deal cyber due diligence to incident readiness, AI governance and secure technology decisions, the focus is simple: understand the risk, decide what matters, make improvement happen, then reassess and repeat.

Intersection

The convergence

Cybersecurity no longer sits in a technical silo. Strategy, technology, software, cloud, data and AI increasingly converge in the same business decisions. A board view of cyber risk that is not grounded in evidence becomes reassurance rather than assurance. Cloud and product decisions that overlook identity, resilience and secure engineering create avoidable exposure. AI adoption without clear rules for data, permissions and human accountability can accelerate that risk.

JandaSec works across those boundaries, connecting board-level risk, business operations and the technology that actually runs the organisation.

Abstract network showing cybersecurity, strategy, technology and AI converging around a central hub
  • Cybersecurity

    Protect what matters, reduce exposure and make the organisation harder to compromise — and faster to recover.

  • Strategy

    Turn cyber risk into clear choices about priorities, investment, accountability and business resilience.

  • Technology

    Bridge strategy and technical reality across commercial IT, SaaS, cloud, software, infrastructure, product and engineering.

  • AI

    Govern AI use, secure AI-enabled products, prepare for AI-accelerated attacks and patch cycles, and use AI defensively — because weak fundamentals are punished faster at machine speed.

Abstract hub showing senior cyber leadership across strategy, technology, cloud, security and AI

Services

Senior cyber leadership where it matters

JandaSec works from strategy, governance and compliance through to engineering, cloud, incident readiness and investment risk. Engagements are shaped around the organisation, its technology and the decisions that matter — not a fixed consultancy playbook.

  • Fractional CISO Leadership

    Experienced CISO leadership without requiring a permanent executive appointment. Strategy, risk, governance, investment, teams, technology and assurance brought together around what the business actually needs.

    Explore
  • Board & Investor Advisory

    Independent challenge and decision support for boards, senior leaders and investors — translating cyber and AI risk into business impact, evidence, investment choices and accountable action.

    Explore
  • Cyber Due Diligence

    Pre-deal cyber due diligence focused on what is being inherited, what could affect the investment thesis and value, and what needs to happen before and after completion.

    Explore
  • Cyber Risk & Improvement

    Evidence-led assessment that turns findings into prioritised risk, owned actions and verified improvement — not a report that is filed and forgotten.

    Explore
  • Incident Readiness & Resilience

    Incident readiness, crisis decision-making, BCDR and recovery preparation designed for the moment plans have to work under real pressure.

    Explore
  • AI Governance & Security

    Practical governance for everyday AI use, AI-enabled products, AI-accelerated attacks and AI-assisted defence — including agents, permissions, data handling, logging and human authority.

    Explore

View all services

Cyber risk thinking

More than a score

Cyber risk is rarely about one control failing in isolation. The useful question is not only “how serious is this?” but “what could this weakness enable, amplify or make harder to recover from?”

JandaSec looks at risk in context: the business, its technology, customers, critical services, growth plans and operating reality. We assess findings for their business significance, the role they could play in an incident and how they interact with other weaknesses. Assumptions, evidence gaps and uncertainty are made explicit. Risk judgements support decisions; they do not pretend to create mathematical certainty.

Abstract global cyber risk view: interconnected systems, evidence panels and decision context

This is not tick-box security. The aim is not to prove that a control exists, but to understand whether it works, what happens when it fails and what that means for the business.

  • Breach Enabler

    Could this weakness help someone gain unauthorised access?

  • Breach Amplifier

    If access is gained, could this increase reach, privilege or damage?

  • Impact Multiplier

    Could this make an incident harder to detect, contain, respond to or recover from?

  • Foundational Weakness

    What underlying conditions are allowing risk to persist or recur?

Cyber incidents rarely come from one spectacular failure.

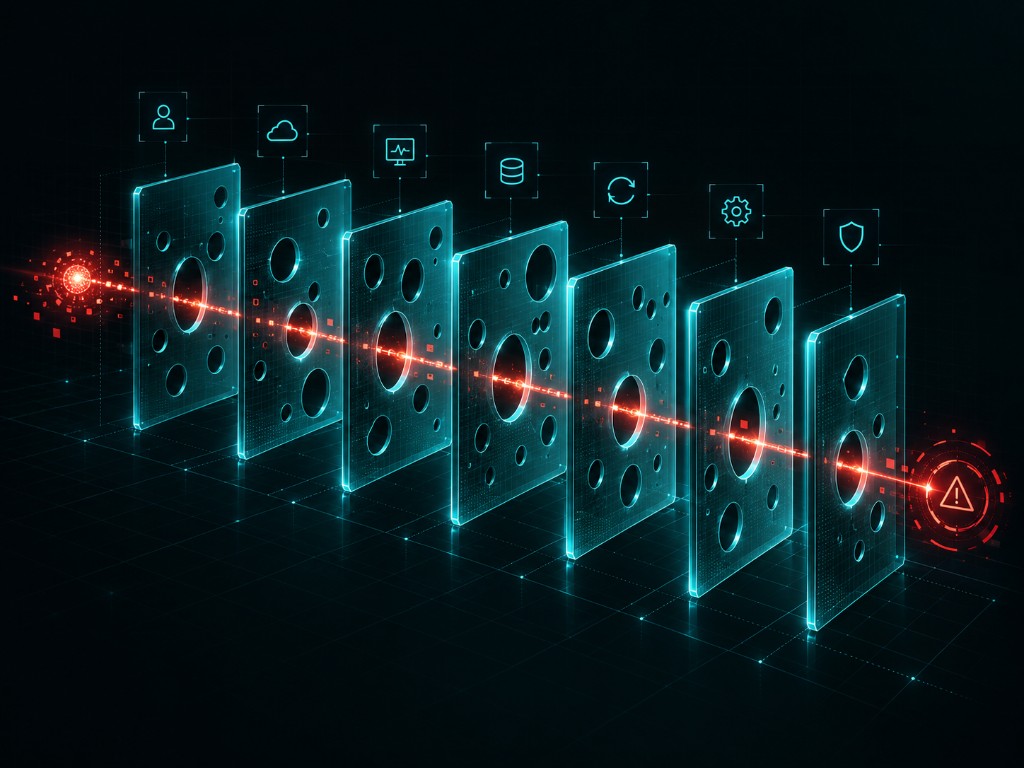
JandaSec uses the Swiss Cheese Model as a reasoning framework for understanding how cyber weaknesses can align. Serious incidents often emerge when several ordinary weaknesses line up: an exposed service creates the route in, excessive privilege increases reach, weak monitoring delays detection and untested recovery turns compromise into prolonged business disruption.

The job is not to pretend every hole can be removed. It is to understand the layers, reduce the chance of weaknesses aligning, strengthen the foundations and know which failures would matter most.

Swiss-cheese style cyber risk layers: weaknesses aligning to create an incident path

Due diligence & investors

Know what you are inheriting. Know what happens next.

Cyber due diligence should support an investment decision, not simply describe the target’s current controls. JandaSec looks at material cyber and technology risk in business context — what could affect the transaction, value creation, resilience or exit, and what practical work should happen before and after completion.
Explore cyber due diligence

Incident readiness

Match-fit for the worst day of the job.

Cyber incidents do not stay inside the security team. They become leadership, operational, legal, customer, communications and recovery problems at the same time.

JandaSec helps organisations prepare before that pressure arrives: clear roles, usable plans, escalation, decision authority, communications, cyber and BCDR dependencies, recovery priorities and rehearsals that expose assumptions while there is still time to fix them.

Assume breach. Limit the damage. Respond calmly. Restore safe trading.

Incident readiness & resilience

Featured conversation · Arcane Link

How prepared is your business for a cyber security incident or ransomware attack?

Andy Latham joins ADL Consulting’s Arcane Link for a practical discussion about what happens when incident response is tested for real — including ransomware, MFA bypass, AI-generated phishing, recovery, security culture and communicating cyber risk at board level.

This player is served by YouTube (privacy-enhanced mode). If it does not load, Watch on YouTube.

AI and innovation

The Four Lenses of AI

Fundamentals still matter. Weak fundamentals are simply punished faster as cyber moves from human-speed to machine-speed.

  • 01

    People using AI

    Approved tools, data handling, retention awareness, human review, transparency and incident reporting.

  • 02

    Attackers using AI

    AI accelerates reconnaissance, social engineering, content generation, attack iteration and vulnerability exploitation. Weak identity, patching, monitoring and awareness are punished faster.

  • 03

    Companies embedding AI

    AI-enabled products and agentic workflows create new identities, permissions, data flows and supplier dependencies. Threat modelling, least privilege, logging, approvals, human authority and kill switches matter.

  • 04

    Defenders using AI

    AI can scale analysis, testing, detection and response, helping make products and systems more secure — but it should strengthen sound engineering and human judgement rather than replace them.

Andy Latham, founder and director of JandaSec Ltd

Experience

Senior judgement backed by technical depth.

Andy Latham

Founder and Director, JandaSec Ltd

JandaSec is led by Andy Latham, an experienced CISO and former CTO with more than 25 years across engineering, software, SaaS, cloud, product, cybersecurity, compliance and executive leadership.

His experience spans permanent and Fractional CISO leadership, board and investor advisory, cyber due diligence, and incident and resilience readiness. Twice recognised as a UK Top 30 CISO, Andy works from board and investment discussions through to the technical detail needed to challenge architecture, engineering and operational assumptions.

Founder-led. Partner-enabled. Built to scale.

JandaSec uses trusted specialist partners where an engagement needs additional testing, implementation or specialist capability. The model is transparent: JandaSec remains accountable for the engagement, with specialist expertise brought in where it genuinely adds value.