Services
Evidence-led cyber risk and continuous improvement
The value is in understanding what is really happening, deciding what matters, converting risk into practical action and knowing when the work is genuinely closed.
What this covers
Business context
Critical services, customers, technology reality, growth plans and operating constraints.
Evidence-led findings
The difference between stated controls and what can actually be shown.
Role classification
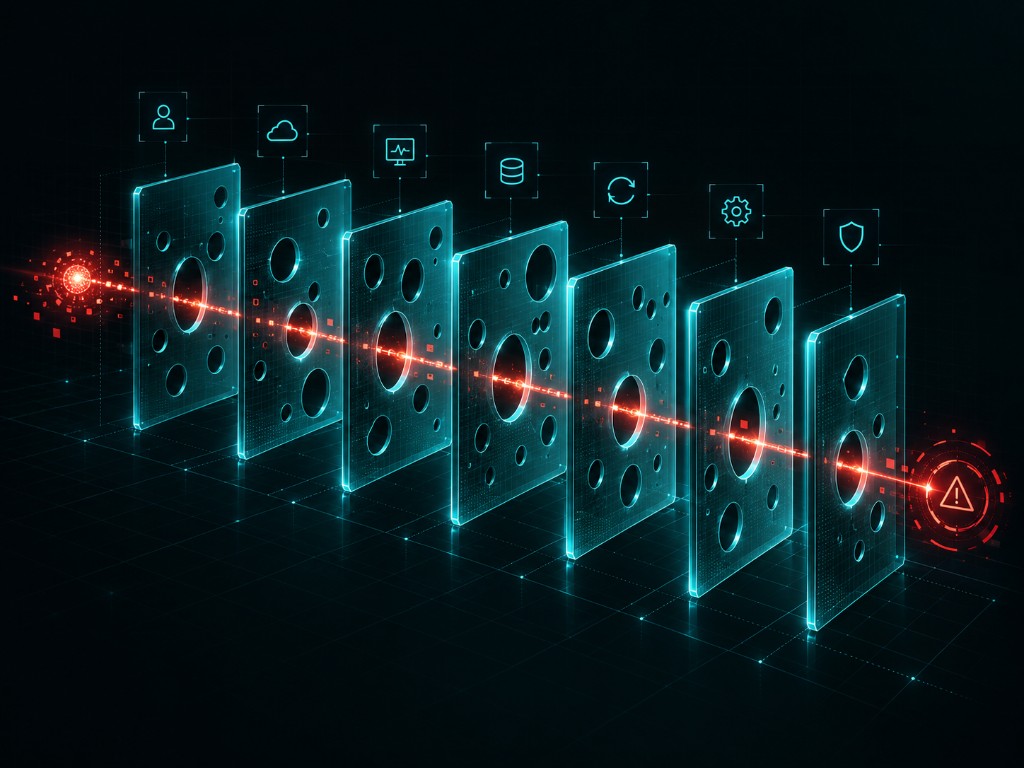
Breach Enabler, Breach Amplifier, Impact Multiplier and Foundational Weakness.
Prioritised action
Immediate exposure separated from longer-term maturity work.
Improvement plan
Owned actions, timing and the evidence required for genuine closure.
Ongoing assurance
Challenge progress, verify closure and preserve observed strengths.
JandaSec does not assess, write a report and disappear. Engagements focus on evidence, role-aware risk classification and a Continuous Security Improvement Plan with ownership, timing and closure evidence.
The method
- Context — Understand the business, technology, customers, critical assets, maturity, constraints and objectives.
- Evidence — Test the difference between stated controls and what can actually be demonstrated.
- Risk — Score severity and classify the role each weakness could play in an attack, incident or assurance failure.
- Priorities — Separate immediate exposure from longer-term maturity improvement.
- Improvement — Turn findings into an actionable plan with ownership and closure evidence.
- Assurance — Challenge progress, verify closure, test readiness and provide evidence rather than unsupported confidence.
Positive assurance
Mature assessment should preserve what works, not only catalogue gaps. JandaSec records Cybersecurity Observed Strengths as well as risks.