AI & technology
AI governance for the way organisations actually use, build and defend with AI
AI is already changing how people work, how software is built, how attackers operate and how security teams defend. JandaSec helps organisations adopt it deliberately — with clear governance, secure engineering, human authority and evidence that the controls actually work. The objective is not AI adoption for its own sake. It is finding where AI can create genuine business value and putting the leadership, engineering and controls around it to use that opportunity well.
Fundamentals still matter. Weak fundamentals are simply punished faster as cyber moves from human-speed to machine-speed.
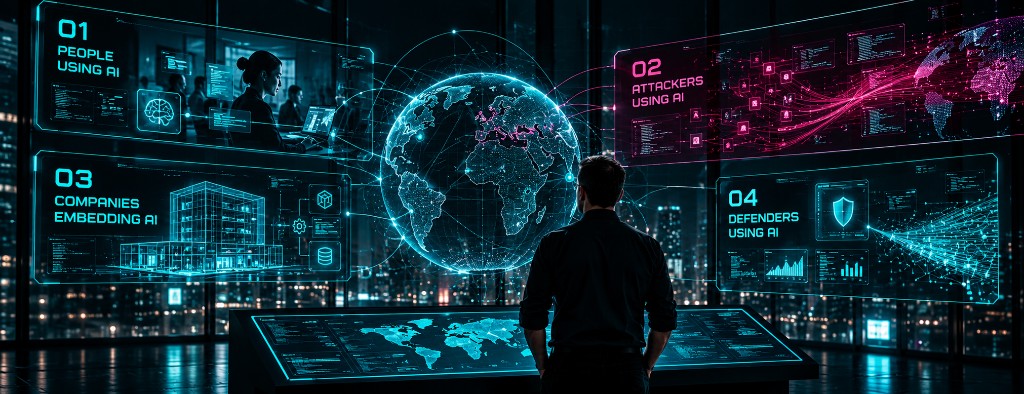
The Four Lenses of AI
01 · People using AI
Approved tools and accounts, data handling, retention, supplier terms, Shadow AI, human review, transparency, training and incident reporting. The organisation should know what AI is being used, by whom, for what purpose and under which controls.
02 · Attackers using AI
AI accelerates reconnaissance, social engineering, content generation, attack iteration and vulnerability exploitation. The underlying weaknesses are familiar — weak identity, exposed systems, slow patching and poor monitoring — but attackers can find and exploit them faster.
03 · Companies embedding AI
AI-enabled products and agentic workflows create new identities, permissions, data flows, dependencies and failure modes. Product AI needs governance across design, threat modelling, data, testing, human oversight, monitoring, change and customer assurance — not simply an acceptable-use policy.
04 · Defenders using AI
AI can accelerate analysis, vulnerability discovery, defensive testing, secure development, detection and response. Used well, it helps defenders work at machine speed too — but outputs still require evidence, engineering discipline and human judgement.
Fractional Chief AI Officer
JandaSec can operate in a Fractional Chief AI Officer capacity, helping organisations turn AI from scattered experimentation into a managed business capability.
The focus is not AI for its own sake. It is identifying where AI can improve productivity, engineering, customer delivery, decision-making and operational effectiveness — then putting in the governance, security and privacy needed to adopt it with confidence.
That means balancing innovation with control: moving quickly where the risk is low, applying deeper review where the impact is higher, and making sure human accountability remains clear as AI systems become more capable and autonomous.
Innovation and productivity. Security and privacy. Governance and accountability. One operating model.
Strategy and value
Identify where AI can create meaningful business value, what should be prioritised, where investment makes sense and how outcomes will be measured.
Adoption and operating model
Turn experimentation into managed adoption through clear ownership, approved tools, decision rights, practical governance, training and safe routes for innovation.
Engineering and product
Connect AI strategy to technical reality across AI-assisted development, agents, product AI, architecture, data flows and secure implementation.
Governance and assurance
Balance innovation with security, privacy, supplier assurance, human oversight, evidence, standards and regulatory readiness.
The job is not to slow AI down. It is to help the organisation move faster without losing control.
Governance that enables adoption
Good AI governance should make responsible adoption easier, not bury it in approval queues.
JandaSec helps organisations turn AI policy into an operating model: clear ownership, approved tools and accounts, controlled experimentation, risk-based approval, supplier assurance, data rules, review dates, training, incident reporting and evidence of what has actually been approved.
Lower-risk uses should be easy to enable. Higher-risk uses should receive deeper review. Decisions should be visible, explainable and revisited as tools, suppliers, data use and capabilities change.
JandaSec can also help establish practical AI governance forums or working groups that bring together security, technology, privacy, legal, commercial, product and business owners without turning every AI decision into a committee exercise.
Agents are identities
Agents are not just smarter chatbots. They are identities with permissions.
Once AI can read files, call APIs, change records, execute code or trigger workflows, governance becomes an identity, access and operational-control problem. Agents need named owners, explicit mandates, least privilege, clear boundaries, audit logs, human approval for sensitive actions, cost controls and a practical way to stop them.
JandaSec helps organisations define those controls before agents quietly accumulate authority that nobody intended to give them.
Automation should inherit controls, not human authority.
AI-assisted engineering
AI coding assistants and software agents can dramatically change engineering speed, but faster code generation does not remove the need for secure engineering.
JandaSec helps teams use AI-assisted development safely: approved developer tooling, protected source code, repository and project instructions, least-privilege agent access, human review, testing, dependency and code security scanning, change control and evidence that generated changes have been validated before release.
AI-generated code should meet the same engineering and security standard as human-generated code.
Give AI the organisation’s rules
AI systems perform better when organisational expectations are made explicit. JandaSec can help define baseline instructions for approved AI tools and agents covering confidentiality, security, professional standards, human authority, verification and secure engineering.
Those instructions can then be adapted to the tool: system instructions, custom instructions, agent rules, project context or repository-level guidance.
Shadow AI is not only about unapproved tools
An organisation can approve an AI platform, buy enterprise licences and still have a visibility gap. The same service used through a personal account may sit outside the organisation’s chosen contractual terms, security settings, retention controls and audit records.
JandaSec looks beyond the application name to the operating context: accounts, identities, workspaces, endpoints, integrations, data flows and the evidence available when something needs to be investigated.
An approved AI platform does not automatically mean approved AI use.
Measure the outcome, not the hype
AI adoption should improve something that matters: speed, quality, customer delivery, engineering effectiveness, learning, operational capacity or risk management.
Seat counts, prompt volumes and token consumption can describe usage, but they do not prove value. Governance should help organisations understand what AI is achieving as well as what risks it introduces.
A Fractional Chief AI Officer should be able to show not only where AI is being used, but where it is improving the business and whether that value justifies the cost, complexity and risk being introduced.
From policy to an auditable operating model
For organisations moving beyond early experimentation, JandaSec can help connect AI governance with existing management systems, assurance and risk processes.
This can include readiness for frameworks such as ISO/IEC 42001, alignment with existing ISO/IEC 27001 and quality-management practices, and helping organisations understand where regulatory requirements such as the EU AI Act may affect their role and AI use cases.
The objective is not compliance theatre. It is an AI operating model that can be explained, evidenced, reviewed and improved.
What JandaSec can help with
Support can range from focused AI governance and security work through to ongoing Fractional Chief AI Officer leadership, connecting strategy, adoption, engineering, value and assurance across the organisation.
AI governance operating model
Policies, ownership, decision rights, approval routes, review cadence, inventories and governance forums that work in practice.
AI tool and supplier assurance
Security, privacy, contractual, data-handling, retention and operational review before AI tools and services are approved.
Shadow AI and account controls
Understand not just which AI services are being used, but whether approved accounts, workspaces and controls are actually in use.
Agentic AI controls
Ownership, identity, permissions, human approvals, auditability, cost controls and emergency disablement for AI agents.
Secure AI-assisted development
Govern AI coding and engineering workflows without weakening peer review, testing, security scanning or release control.
AI assurance and maturity
Evidence, review, internal assurance and management-system thinking that help AI governance mature beyond policy documents.
Boundary
JandaSec provides AI governance, security, assurance and technology advisory support. This does not replace legal advice, regulatory counsel, specialist model-safety research, product certification or independent conformity assessment where those are required.
The aim is to help organisations understand the technology, govern it credibly and make better decisions about how AI is used, built and secured.
A Fractional Chief AI Officer engagement does not transfer executive accountability away from the client organisation. Boards, executives, product owners, technology leaders and other accountable roles retain their own decision-making authority unless a separate appointment explicitly changes that position.